
What is changing?
Strong Customer Authentication (SCA) will become mandatory under the new European Payment Service Directive (PSD2). It is being introduced to help prevent fraud across online and remote card payments, affecting Ecommerce and Contactless transactions.
Once introduced, Merchants need to be able to accept a two-factor authentication process at checkout to remain compliant. If the required level of authentication is not provided to card-issuing banks when required, then transactions will be declined.
To comply with the new SCA rules, payments can be processed using 3DS2. Where 3DS2 is not yet supported, then 3DS1 will be used as a fallback to ensure SCA compliance is maintained.
To read more about SCA, how it will affect your customers and how to remain compliant, then please read our dedicated page on our website
What are the next steps?
As part of Monek’s on-going commitment to provide our merchants with a robust, safe and secure solution which requires minimal maintenance, we have spent the past weeks and months looking for ways to ensure a hassle-free upgrade to SCA and its components.
1) Enrolment into 3DS1
Monek has registered all ecommerce merchants for 3DS1. We are completing the final steps of the testing & implementation process for 3DS1 and we will advise you when 3DS1 is available for you to switch on. You may switch it on before 14th September or it will be done for you by Monek on the date.
2) SecureHosting: API Merchants – You host your own payment page**
API merchants are not required to make any changes at all to facilitate 3DS2 for ecommerce payments. All that we would recommend that you ask your technical teams to review and confirm is that ‘CardholderName’ is being submitted with the transaction at all times, as this is a mandatory field under 3DS2.
Please refer to the relevant section in the Secure Hosting documentation
3) SecureHosting: Hosted page merchants – We host the payment page for you
Hosted page merchants are not required to make any changes. We will automatically upgrade you on 14th September.
4) Optional updates for all SecureHosting merchants
You may wish to include the below optional fields in your transaction request/on your payment page as it may streamline the customer journey – the more information you provide about the cardholder upfront, the less likely they will be required to provide additional information during authentication with their card issuer.
- Billing Address
- Cardholder Email
- Cardholder Phone
- Shipping Address
We expect that the majority of merchants will have already been providing these fields as standard, but you may wish to verify this with your technical teams.
Time Line
In the UK from June 1st 2021, card approval schemes will begin soft-checking for valid 3DS2 data, rerouting to 3DS1 (the current version of 3DS) if that isn’t found.
However from the 14th September 2021, 3DS2 will be strictly enforced in the UK with transactions missing this security data being rejected.
Note Monek 3DS2 – is in final testing and will be live prior to the 1st of May 2021
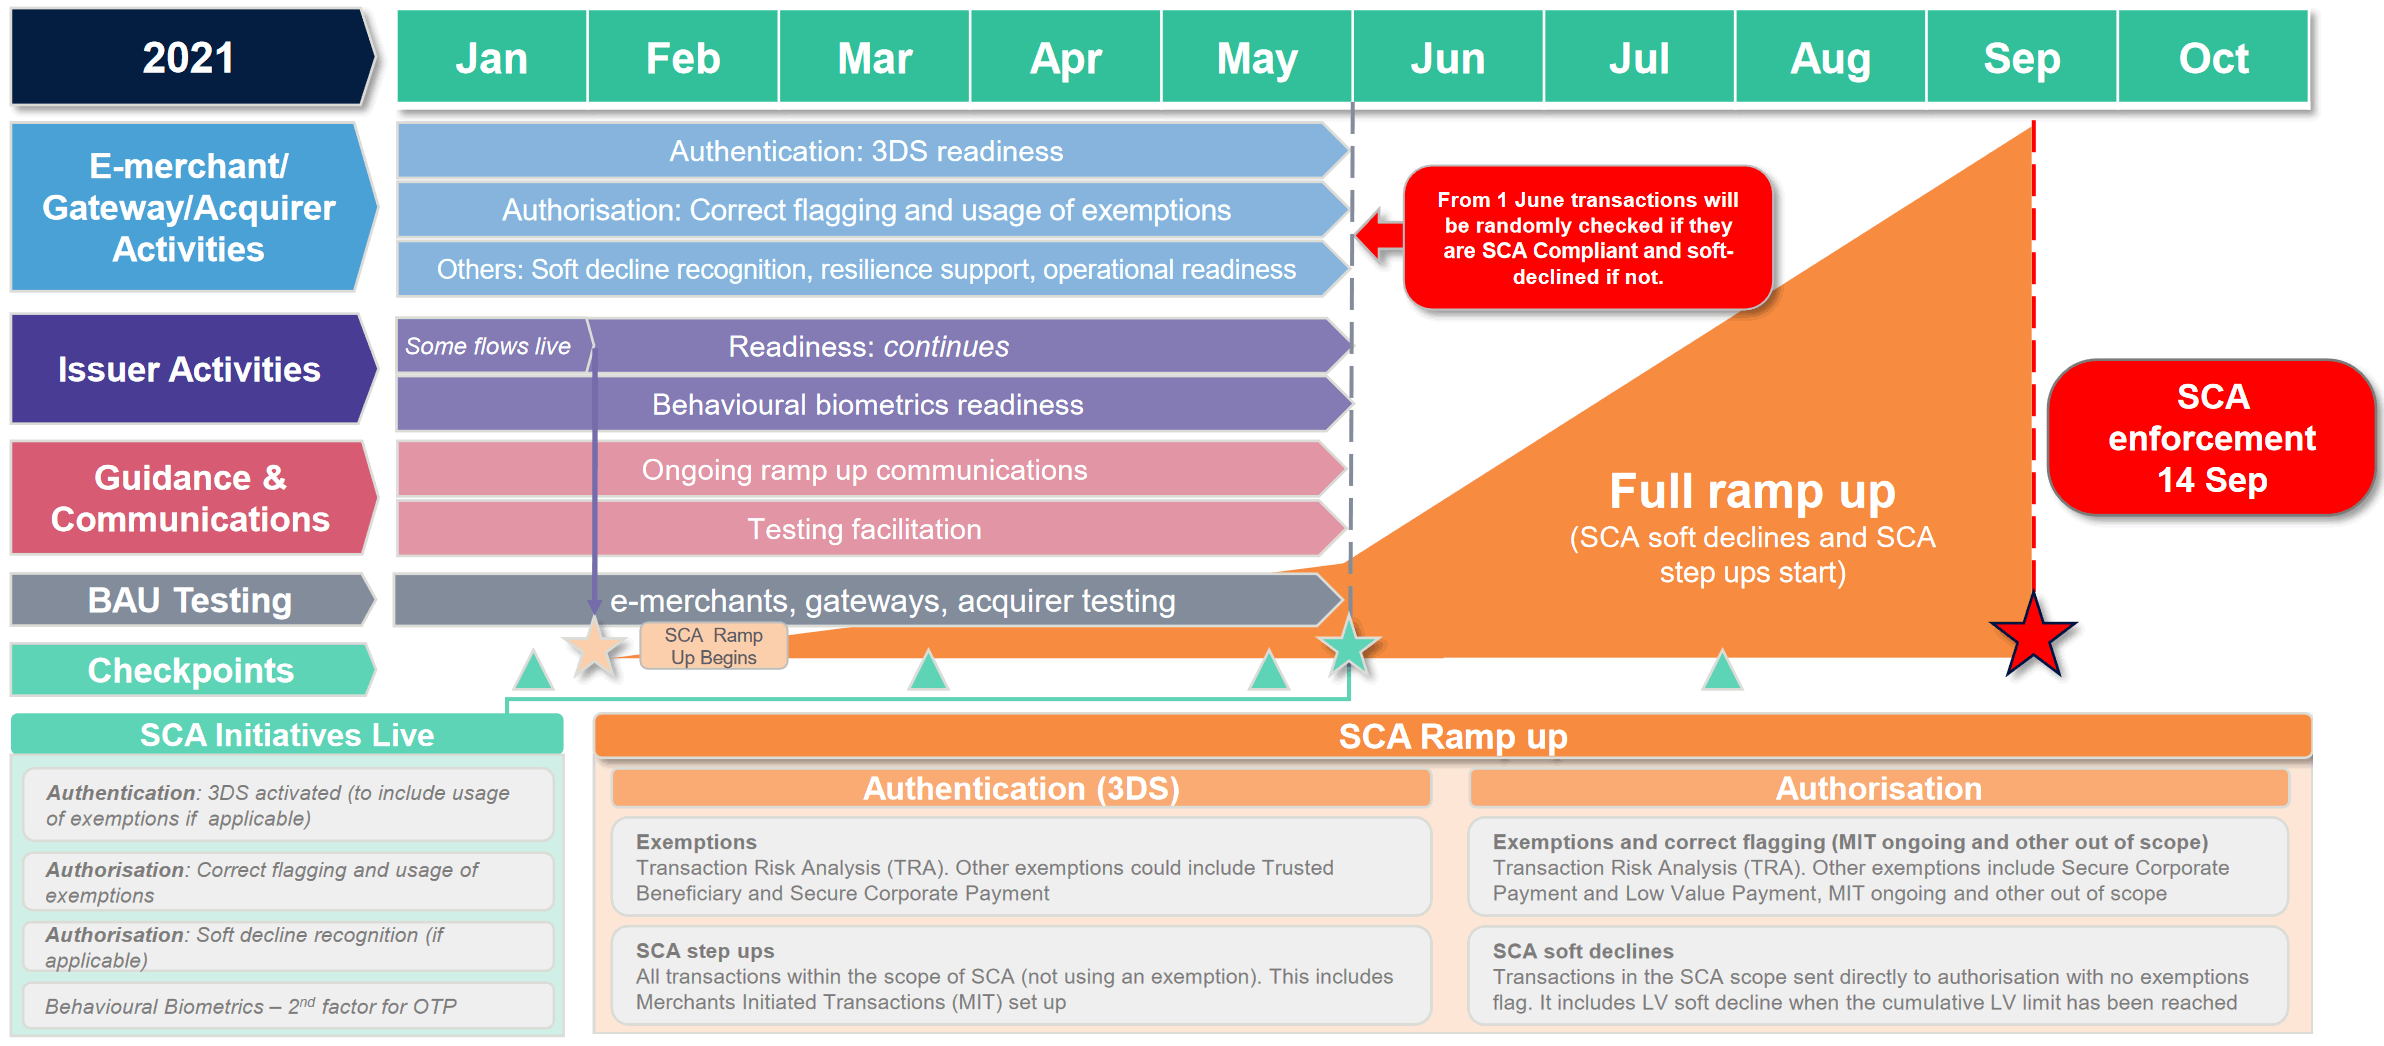
Exemptions
At present, limited agreed transaction exemptions are available. Once we receive any further clarification, we will update you.
UK finance Guides:
 UK Implementation and ramp up plan
